What Is Kubescape? Scanning Kubernetes for Real Security Risks — Thunder with Ben Hirschberg
Associated Thunder episode: What Is Kubescape? Scanning Kubernetes for Real Security Risks
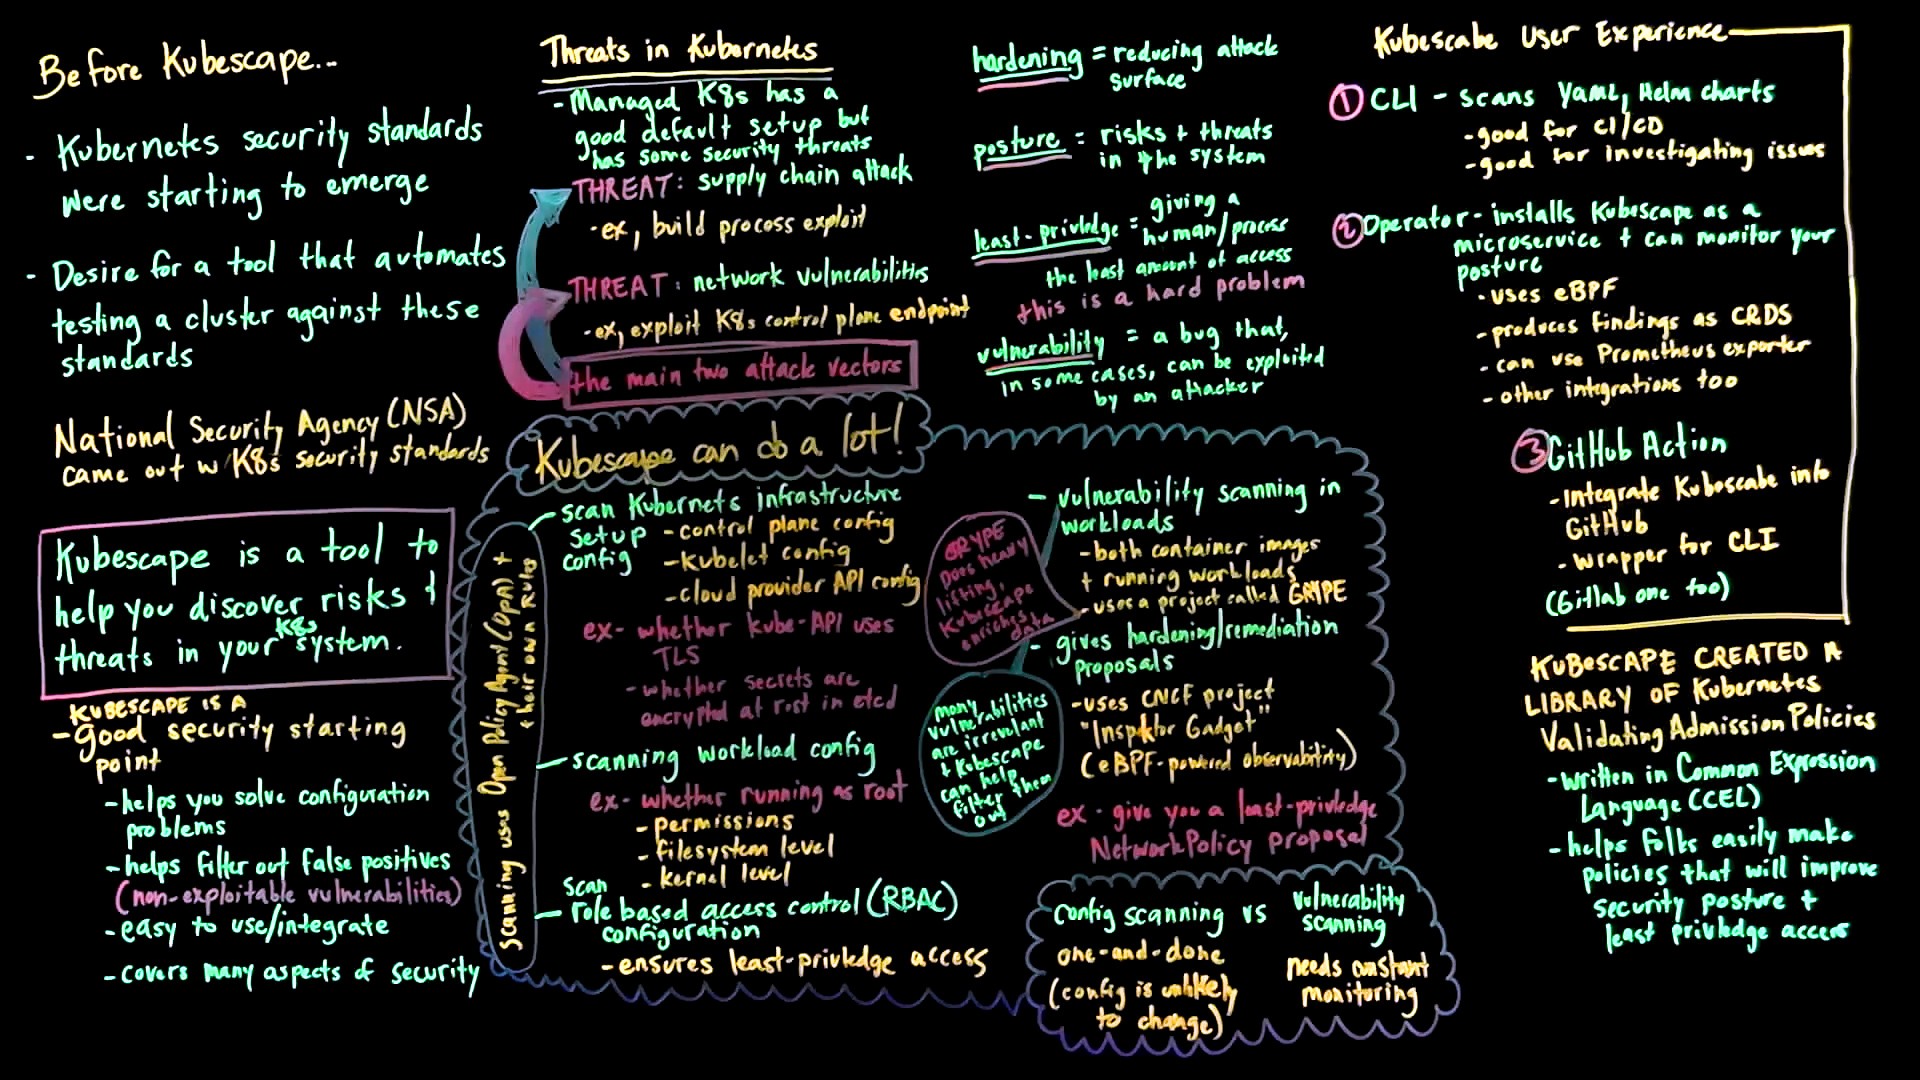
- Kubernetes security standards were starting to emerge
- Desire for a tool that automates testing a cluster against these standards
National Security Agency (NSA) came out with Kubernetes security standards
Kubescape is a tool to help you discover risks and threats in your Kubernetes system.
- Kubescape is a good security starting point
- Helps you solve configuration problems
- Helps filter out false positives (non-exploitable vulnerabilities)
- Easy to use/integrate
- Covers many aspects of security
Managed Kubernetes has a good default setup but has some security threats.
The main two attack vectors:
- Threat: supply chain attack
- Threat: network vulnerabilities
- Example: exploit Kubernetes control plane endpoint
- Scan Kubernetes infrastructure setup
- Control plane config
- Kubelet config
- Cloud provider API config
- Example
- Whether kube-API uses TLS
- Whether secrets are encrypted at rest in etcd
- Example
- Scanning workload config
- Example
- Whether running it as root
- Permissions
- Filesystem level
- Kernel level
- Example
- Scan role based access control (RBAC) configuration
- Ensures least-privilege access
Scanning uses Open Policy Agent (OPA) and their own rules
- Vulnerability scanning in workloads
- Both container images and running workloads use a project called GRYPE
- GRYPE does the heavy lifting. Kubescape enriches data
- Many vulnerabilities are irrelevant, and Kubescape can help filter them out
- Gives hardening/remediation proposals
- Uses CNCF project "Inspektor Gadget" (eBPF-powered observability)
- Example: gives you a least-privileged NetworkPolicy proposal
Config Scanning vs Vulnerability Scanning
- Config Scanning is one and done. Config is unlikely to change.
- Vulnerability Scanning needs constant monitoring.
hardening = reducing attack surface
posture = risks & threats in the system
least-privilege = giving a human/process the least amount of access — this is a hard problem
vulnerability = a bug that, in some cases, can be exploited by an attacker
- CLI - scans YAML, Helm charts
- Good for CI/CD
- Good for investigating issues
- Operator - installs Kubescape as a microservice & can monitor your posture
- Uses eBPF
- Produces findings as CRDs
- Can use Prometheus exporter
- Other integrations too
- GitHub Action
- Integrate Kubescape into GitHub
- Wrapper for CLI
- There is a GitLab one too.
Kubescape created a library of Kubernetes Validating Admission Policies
- Written in Common Expression Language (CEL)
- Helps folks easily make policies that will improve security posture & least-privilege access