Associated Datadog Illuminated episode: How Datadog Detects Malicious Code at Scale
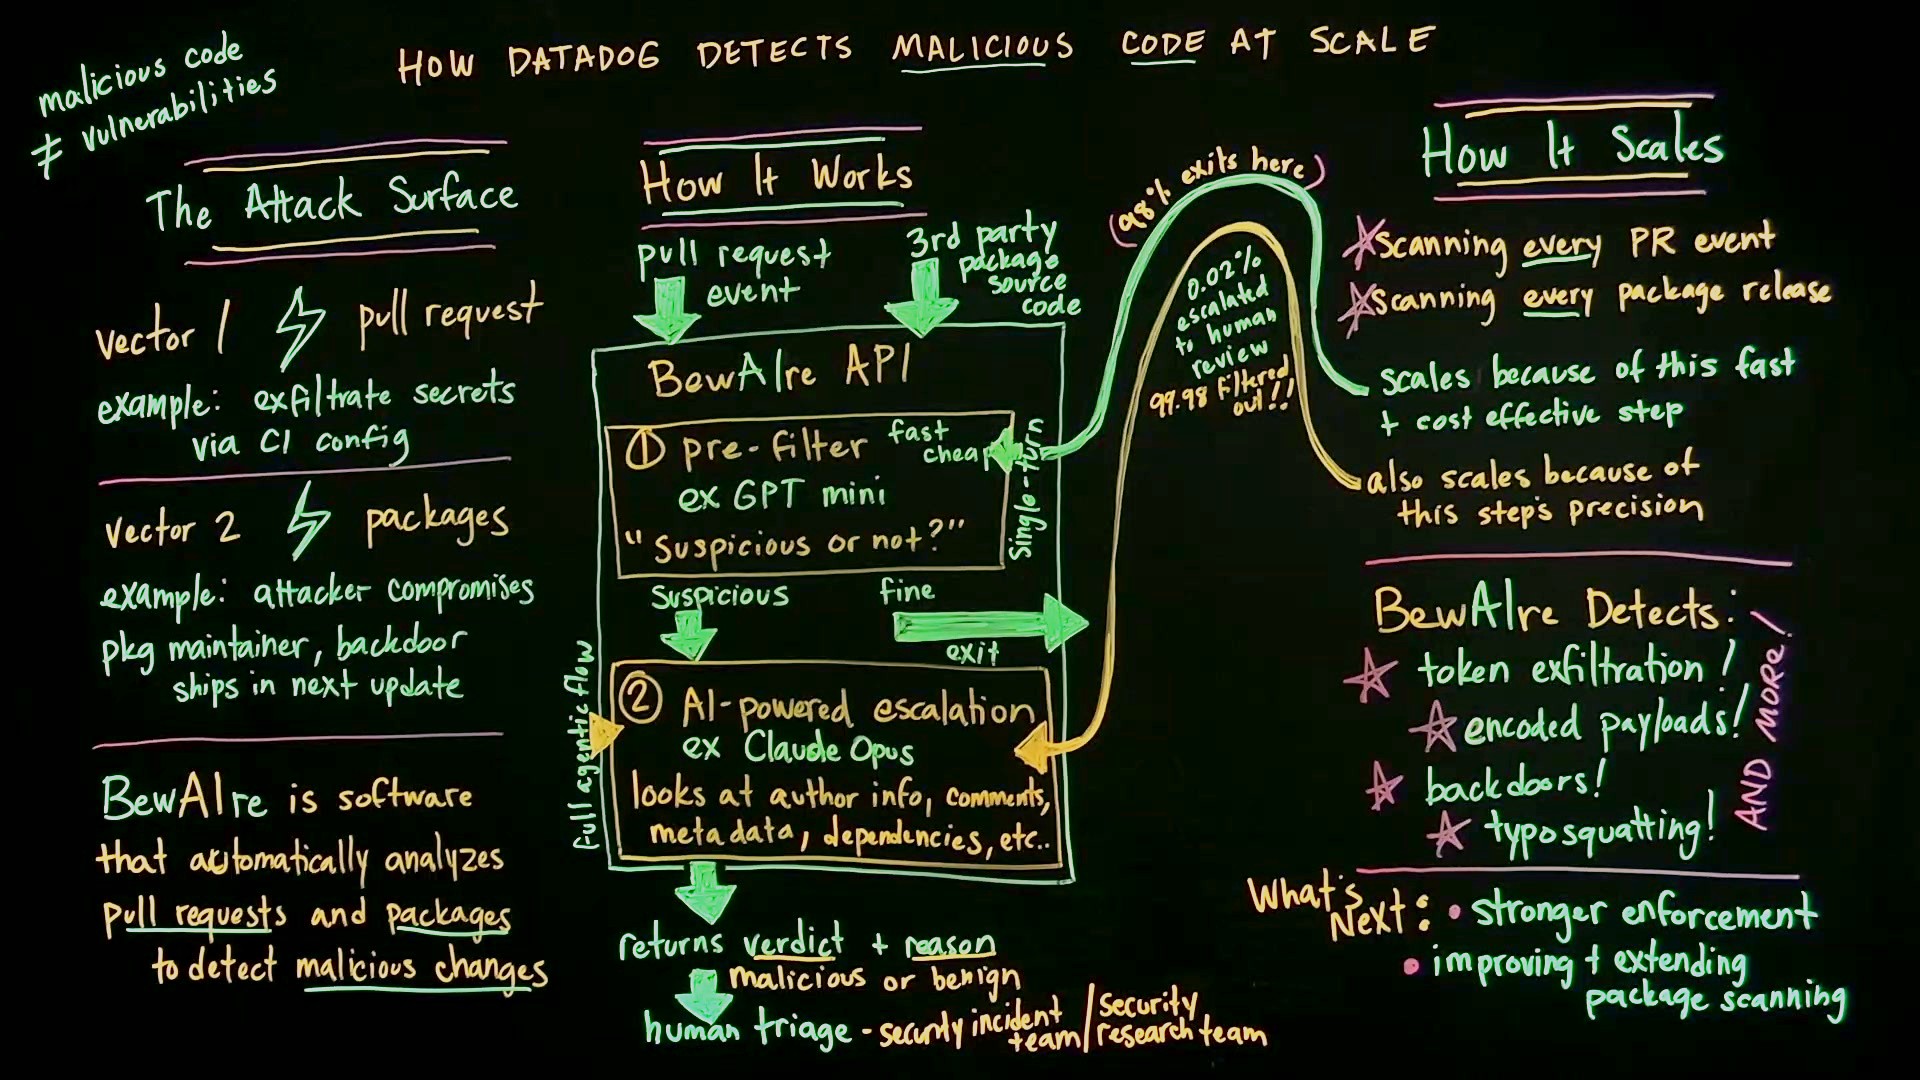
malicious code ≠ vulnerabilities
- Vector 1 ⚡ pull request
- example: exfiltrate secrets via CI config
- Vector 2 ⚡ packages
- example: attacker compromises package maintainer, backdoor ships in next update
BewAIre is software that automatically analyzes pull requests and packages to detect malicious changes
flowchart TD
PR["pull request event"] --> API
PKG["3rd party package source code"] --> API
subgraph API["BewAIre API"]
direction TB
F["① pre-filter — fast, cheap<br/>ex GPT mini<br/>"Suspicious or not?"<br/>(single-turn)"]
E["② AI-powered escalation<br/>ex Claude Opus<br/>looks at author info, comments,<br/>metadata, dependencies, etc..<br/>(full agentic flow)"]
F -- suspicious --> E
F -- "fine — 99.98% filtered out" --> EXIT["exit"]
end
E -- "0.02% escalated to human review" --> V["returns verdict + reason<br/>malicious or benign"]
V --> H["human triage — security incident team / security research team"]
☆ Scanning every PR event
☆ Scanning every package release
scales because of the fast + cost effective step 1 ↑
also scales because of step 2's precision ↑
☆ token exfiltration!
☆ encoded payloads!
☆ backdoors!
☆ typosquatting!
AND MORE!
- stronger enforcement
- improving + extending package scanning